Ben Andrews — Chartered Cyber Security Professional
Cyber risk,made clearfor the boardroom.
Twenty years designing and delivering the cyber strategies, operating models and assurance that regulators trust and boards act on — for critical infrastructure, the public sector and growing businesses.
Years in governance, risk & compliance
Regulatory funding secured for a client
Authority documents authored
Professional credentials, incl. Chartered status
Selected work
Outcomes that speak for themselves.
A few engagements I’m proud of. Client names are kept confidential — the results aren’t. Select any project to read the story.
Expertise
Director-level GRC, end to end.
From the first gap analysis to verified remediation and handover — one senior partner who has done it before, at scale, in regulated environments.
Strategy & operating models
Target Operating Models and multi-year Security Improvement Programmes aligned to ISO 27001, CAF, SEC and NIS.
Risk management
Quantitative and qualitative methods aligned to ISO 27005 and NIST, translated into clear business impact and owned risk.
Audit & assurance
Risk-based audit plans, defensible evidence packs and remediation roadmaps that actually get findings closed.
Board advisory
Board-level risk reporting, KPIs and KRIs, and investment cases that turn cyber risk into confident decisions.
Service & product innovation
New consultancy service lines and cloud compliance products — designed, launched and scaled.
Leadership & mentoring
Building and developing high-performing GRC teams, with a focus on capability uplift and succession.
Experience
Two decades in regulated environments.
Ben Andrews Consultancy
Owner / Operator
Cydea
Principal Consultant (Director)
KMG Health Partners
Director of IT & Client Services
University Centre Weston
Cyber Security Associate Lecturer
Avon and Somerset Police
Cyber Protect
Remploy Ltd
Consultant
CINCH
Founder
Avon and Somerset Probation Trust
GRC Manager
Serco
GRC Manager
Credentials & memberships
Chartered Cyber Security Professional — Risk & Governance
UK Cyber Security Council
Full Member
Chartered Institute of Information Security
Cyber Security, Distinction
University of the West of England
Certified Information Systems Security Professional
ISC2
Certified Security Analyst
EC-Council
Lead Auditor
ISO/IEC 27001
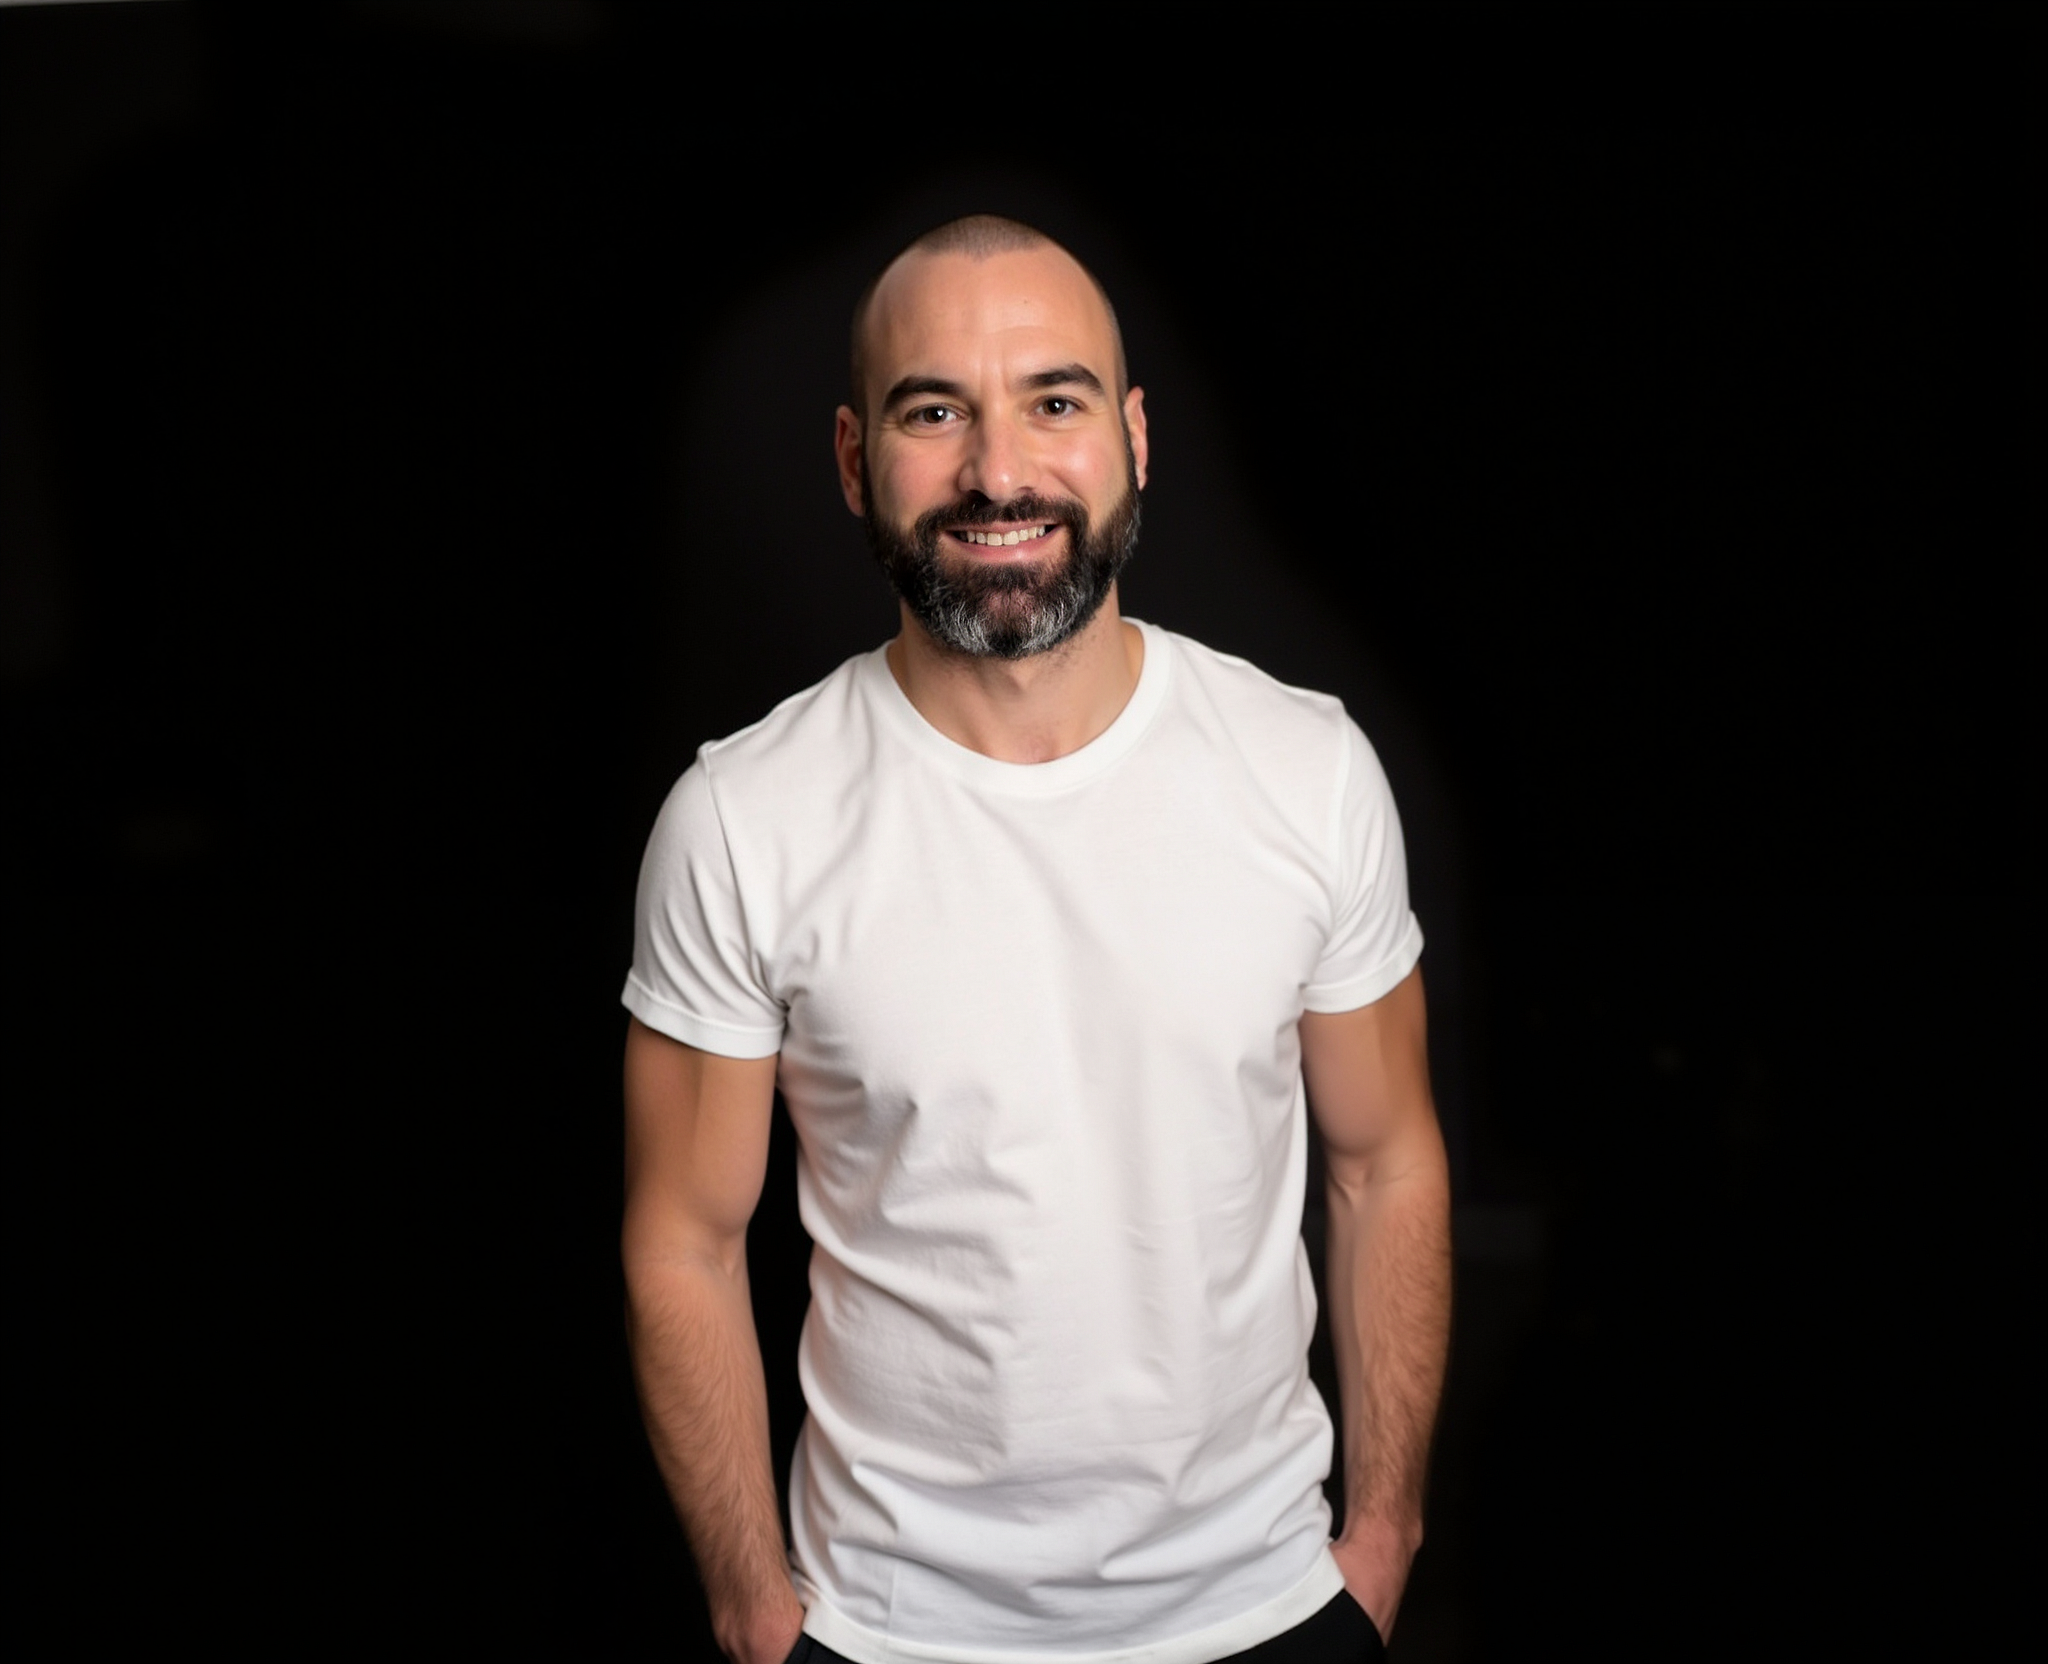
About
A trusted advisor to boards and regulators.
I’m Ben Andrews — a chartered cyber security executive with over 20 years of cross-sector experience in governance, risk and compliance. I design and deliver new cyber capabilities at scale, lead complex transformation programmes and align security strategy with what the business is actually trying to achieve.
Alongside client work, I’m a regular speaker and mentor in cyber security education, and have developed training for law enforcement, higher education and industry — including curriculum design and red/blue team exercises for degree programmes.
Contact
Let’s talk about what’s at stake.
Tell me a little about your organisation and what you’re working through. I read every message personally and reply within two working days.